AI architecture · Standards explainer
Connect agents without losing control
Understand how MCP and A2A support agent integration, where governance belongs, and which claims require proof before production use.
Agents become more useful when they can reach approved tools, data, and other systems. They also become harder to control.
Integration standards can reduce custom connection work. They do not decide what an agent may access, which action is safe, or who is accountable for the result.
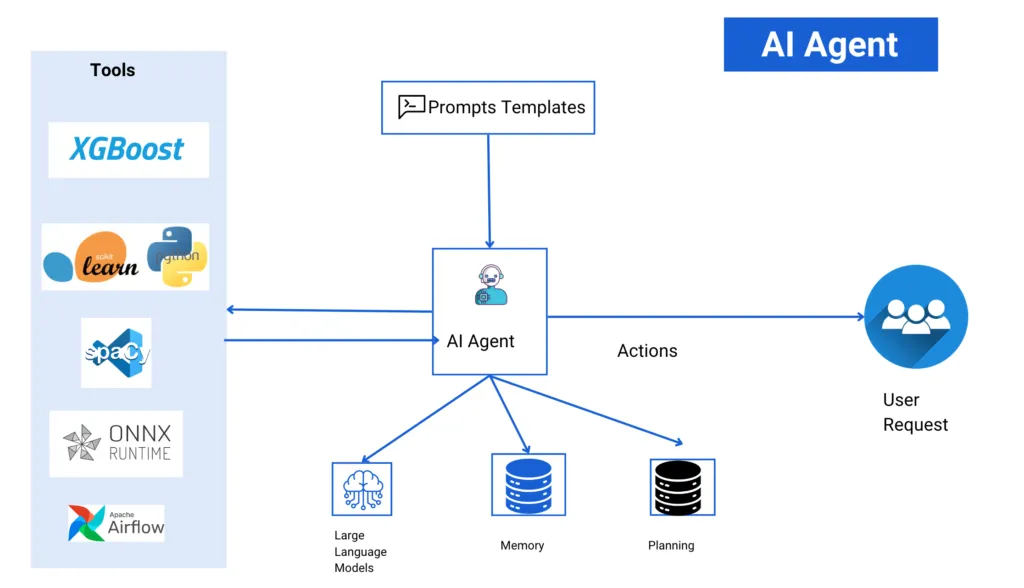
MCP connects an AI application to context and tools
The Model Context Protocol, or MCP, defines a common interface for compatible AI applications. An MCP server can expose resources, prompts, and tools through that interface.
That interface can reduce one-off integration code. It also creates a boundary that needs deliberate controls:
- authenticate the client and server
- expose only the required tools and resources
- validate tool inputs and outputs
- separate read operations from writes
- record calls without leaking secrets or personal data
- handle unavailable or untrusted servers
Microsoft documents current MCP and A2A availability in its Foundry Agent Toolbox overview. Check supported authentication, regions, network controls, and preview status for the deployment you plan.
A2A coordinates compatible agent systems
Agent-to-Agent, or A2A, is intended for communication between agents or agent platforms. It can describe capabilities, exchange messages, and coordinate work without requiring each pair to use a private protocol.
That does not mean every participating agent should trust every other agent. Treat each connection as an external system boundary. Verify identity, permitted tasks, data classification, timeout behaviour, and the response to partial failure.
Microsoft’s A2A announcement explains the intended interoperability direction. Production support depends on the products and versions at each end.
Governance sits above the protocol
MCP and A2A move messages and capabilities. Your organisation must still supply:
- role and workload identities
- least-privilege access
- policy enforcement
- human approval
- data-loss controls
- trace and retention rules
- incident ownership
Put those controls around the action, not only around the chat interface. An agent that can draft a change is different from an agent that can execute it.
Design for failure before scale
Multi-agent systems add failure paths that a single workflow does not have. One agent may time out, return an incompatible format, repeat a request, or act on stale context.
Before production, test:
- unavailable tools and agents
- conflicting responses
- duplicate or delayed messages
- revoked permission
- unsafe or malformed tool arguments
- an escalation that receives no response
The result should be a defined state, not an improvised retry loop.
Keep case evidence separate from protocol claims
The Odie Bot case study shows how a virtual helpdesk can improve access to a public-data service. The published story does not establish that the solution used MCP, A2A, or today’s Foundry architecture.
Use the case for the outcome it documents. Use current Microsoft documentation and your own test evidence for protocol and platform claims.
Integration is ready when the team can explain who connects, what crosses the boundary, which actions are allowed, and how the system stops safely.
AI
Agentic AI: From Prototype to Production
Plan the move from an agent demo to production with testing, monitoring, integration, governance, training, and measurable outcomes.
AI
Agentic AI Adoption: Governance from the Start
See how enterprise teams can connect agent design, human escalation, observability, policy controls, and outcome measurement.
AI
Agent Observability: What Enterprises Should Record
Learn how action monitoring, decision traces, evaluation loops, governance controls, and CI/CD checks support reliable AI agents.
Design the integration and the control path together
Map identities, data, tools, approvals, telemetry, and failure handling before connecting agents.